AccessOps
Automated employee offboarding that proves the person's access is really gone. When someone leaves, an HR event shuts off their access in Microsoft Entra ID, Keycloak and an Active Directory-compatible directory, and each system is checked to confirm the change.
- 2.6 sfrom the HR event to the person signed out and their tokens blocked
- 6gaps found by live testing, each fixed or documented
- 20 sfor Microsoft Entra ID to confirm the change, in a test tenant
- 32 sto catch a sign-in after someone has left and alert the security team
Key decisionMeasure what disabling an account leaves behind instead of assuming it, and never let a statement count as proof.
What it shows
Real identity systems
Offboarding runs against Microsoft Entra ID (through Microsoft Graph), Keycloak and a Samba directory, not mock-ups.
Testing that finds real gaps
Before-and-after checks found 6 gaps, like sessions and Kerberos tickets that kept working after the account was disabled.
Security engineering
MFA for operators, policy checks that deny when unsure, signing-key rotation and a leaked-key drill.
Audit-ready controls
Nobody can close their own case, every step records its proof, and controls map to NIST SP 800-53.
How it works
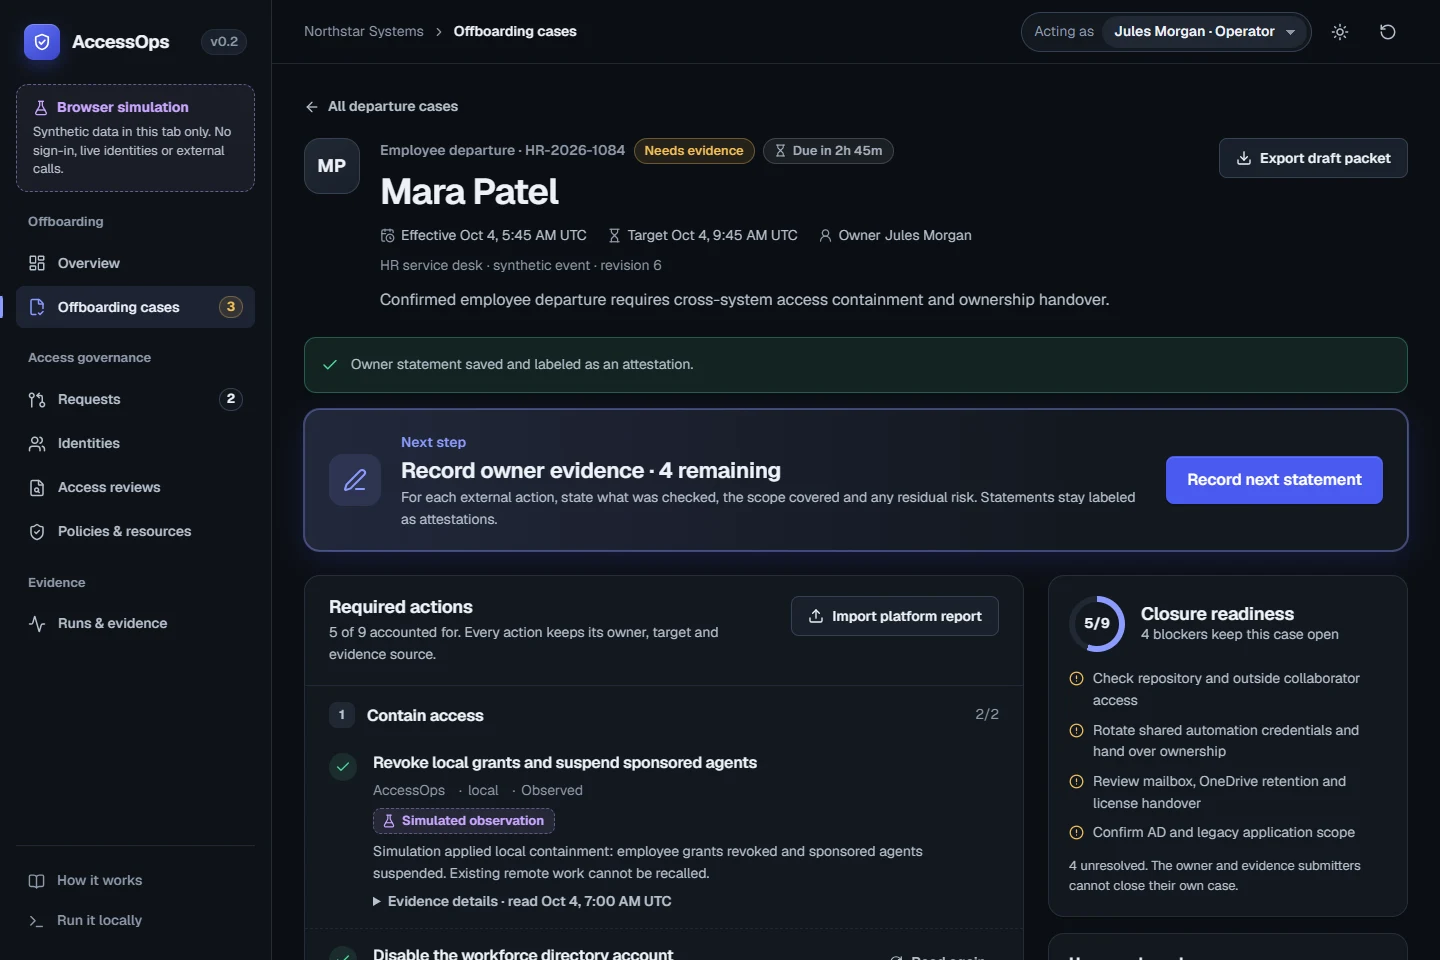
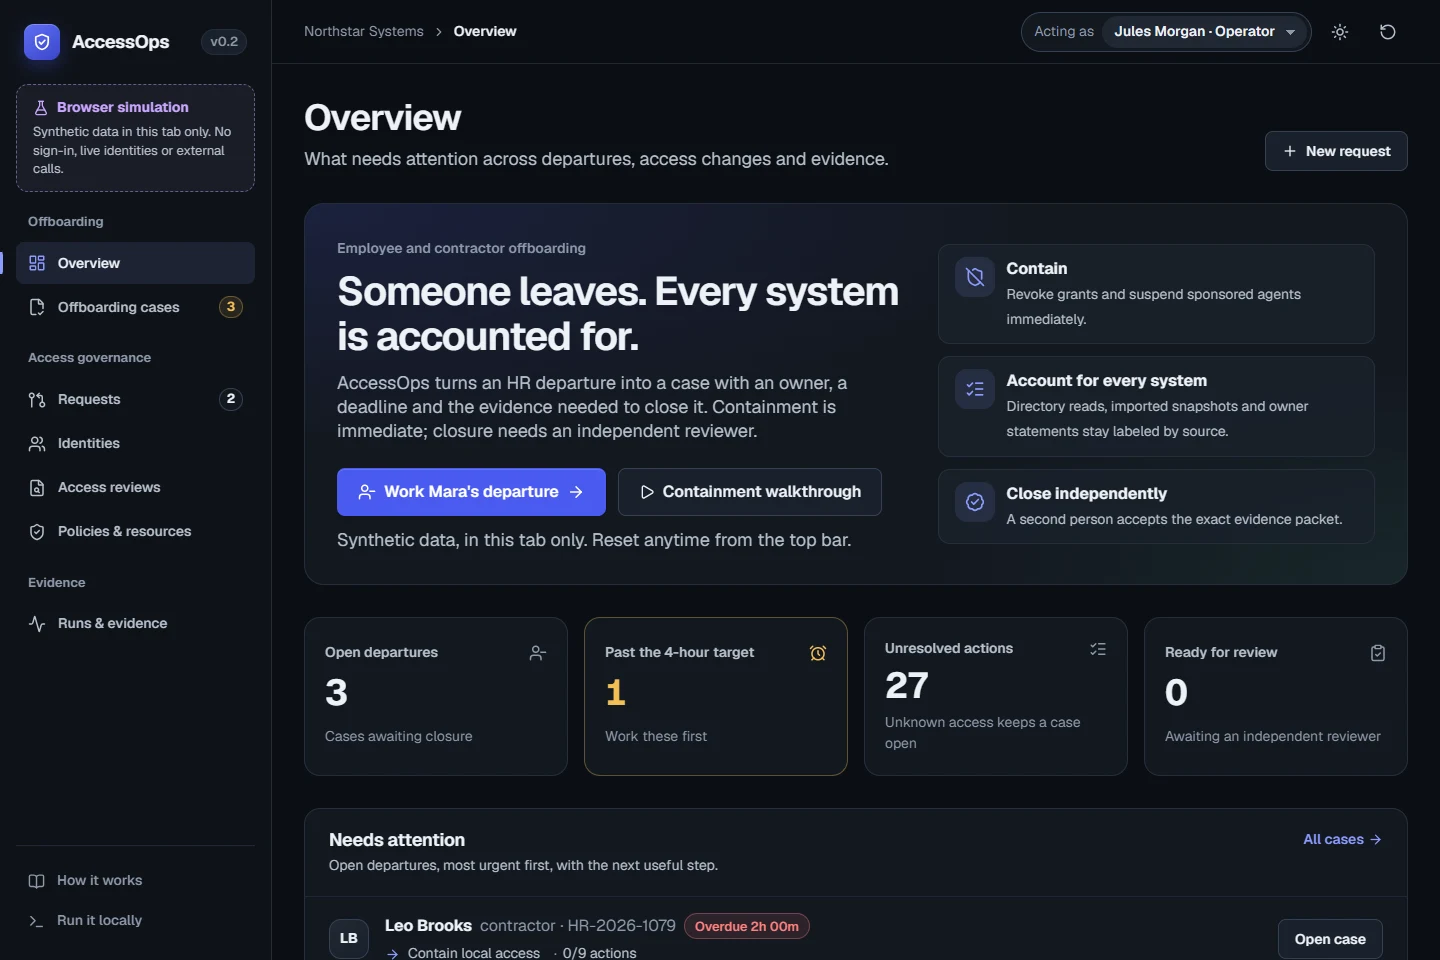
Offboarding usually ends when someone disables the main account. AccessOps turns each departure into a case with an owner, a four-hour target and a step for every system the person could still reach.
Keycloak and the directory run in a local Docker lab; Entra is a free test tenant. The public demo is a separate browser simulation and never calls either.
Explore the case flow Choose a stage
Stage 01 / Shut off access
Can the person still act right now?
One step disables the account, removes group rights, ends sessions and suspends any automated agents the person sponsors. Apps that check tokens themselves get a signed signal to refuse the person's tokens.
Work an agent already started is not recalled.
Stage 02 / Check it worked
Did each system actually change?
Each system is read again before the step counts. For a day afterward, any sign-in by the person blocks closure until someone investigates it.
Unknown, partial or two-hour-old readings keep the step open.
Stage 03 / Track the rest
What can't be reached directly?
GitHub, Microsoft 365 handover and shared credentials become steps with an owner. Imported reports and owner statements are labeled as what they are.
Missing from a GitHub list doesn't prove access was removed.
Stage 04 / Close
Who can say it's done?
Someone who doesn't own the case reviews the exact evidence and closes it. The closed record can't be changed.
Closure records reviewed evidence; it doesn't prove every copy or session is gone.
What testing found
Each gap came from a check that failed against the live systems. The failed runs stay published next to the fix.
| Gap | Before the fix | Now |
|---|---|---|
| Group membership | Stayed after the account was disabled | Every grant is removed and re-checked |
| App sessions | The person stayed signed in to the app | Sessions end; done only at zero |
| Tokens apps check themselves | Accepted for 2 more minutes | Refused 3 s after the cut-off |
| A leaked signing key | A forged token was accepted; apps trusted a removed key for 5 minutes | Apps drop a removed key in 60 s |
| Key rotation | Valid tokens refused for 30 s | New key published first; none refused |
| Kerberos tickets | Kept the removed group's rights | Can't be revoked; the case shows when they expire (up to 10 h) |
One failed check was right. The test backdated a departure and then signed in, which counts as access after departure. The test changed, not the rule.
Results
October 5, 2026, with synthetic users. Every live suite passed on its latest run.
| Check | Passed |
|---|---|
| Departure case through Keycloak | 18 / 18 |
| Departure case with a Samba directory account | 28 / 28 |
| Sessions and tokens, before and after | 22 / 22 |
| HR event to access shut off | 10 / 10 |
| Microsoft Entra ID, free test tenant | 11 / 11 |
| Sign-in after departure | 7 / 7 |
| Operator MFA | 14 / 14 |
| Key rotation and leaked-key drill | 13 / 13 |
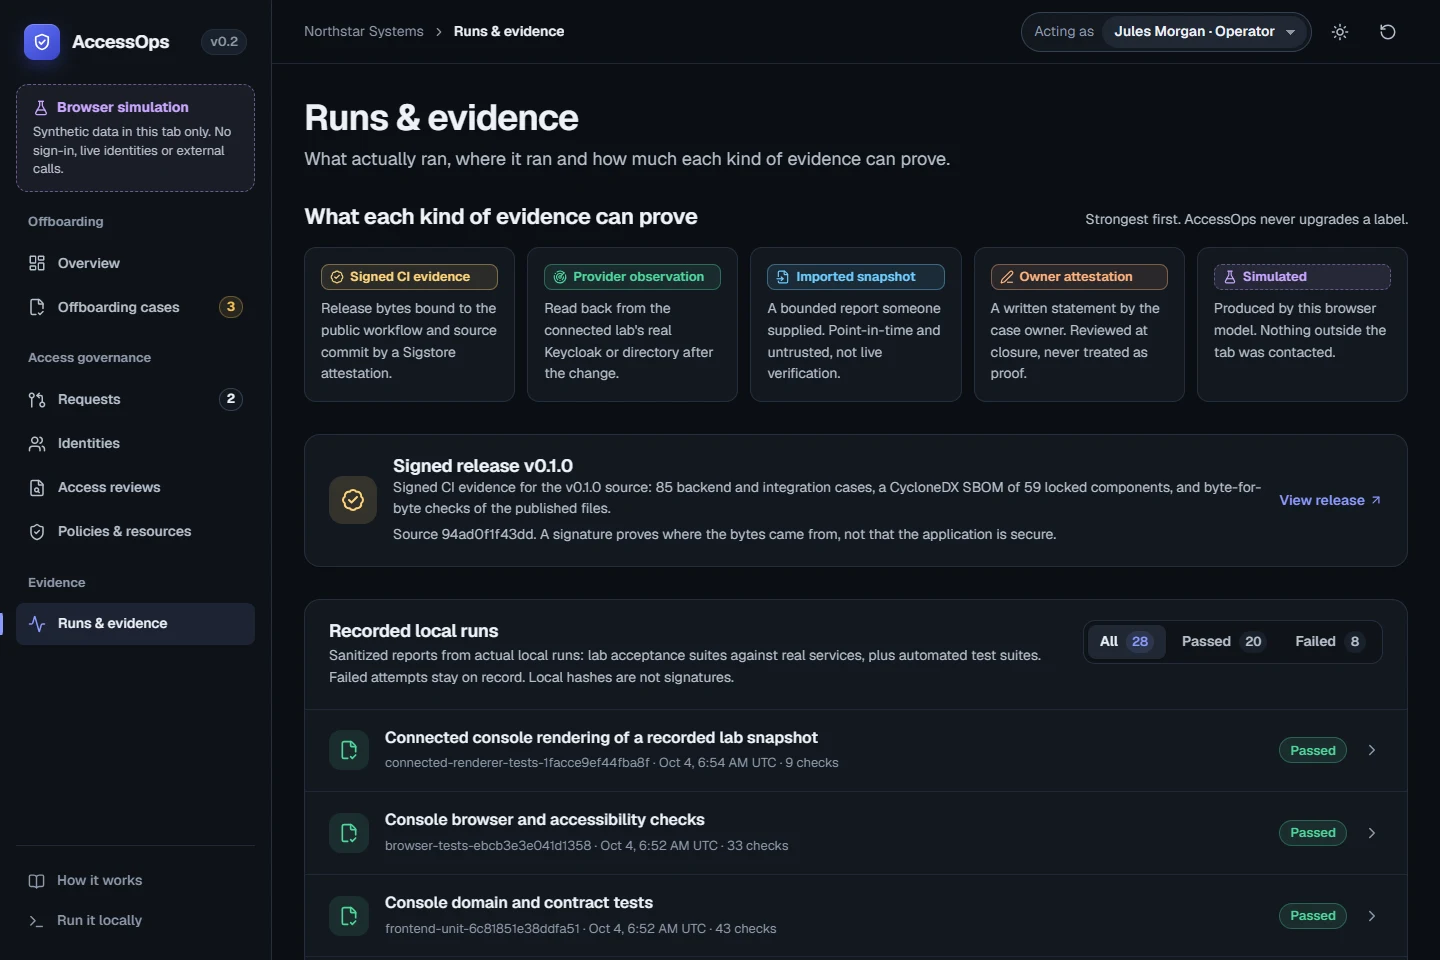
| Signed v0.4.0 release (GitHub CI) | 401 / 401, provenance and SBOM verified |
Signed v0.4.0 release · Verification ledger · Recorded runs in the demo
Design choices
Proof labels that never upgrade
Each step shows where its proof came from: a live reading, an imported report, an owner statement or the browser simulation.
Approvals tied to the exact change
New access needs a second person's approval for that exact change, valid for 15 minutes. Cutting access needs none.
Connectors limited to their own objects
The directory and Entra connectors can touch only their test objects; live runs confirmed they refuse anything else.
One next step per case
Each case shows the next step and who can take it, in dark and light themes checked for accessibility.
Limits
- Synthetic users in a lab and a free Entra test tenant; not a production deployment.
- Samba stands in for Active Directory, so results don't prove Microsoft AD behaves the same.
- GitHub and Microsoft 365 are offline sample data, not live connections.
- Entra sign-in logs need a paid tier, so sign-ins after departure are watched in Keycloak only.
- Kerberos tickets issued before offboarding work until they expire, up to 10 hours.
- Apps that check tokens themselves refuse early only if they follow AccessOps' signals.
- Operators use app-based one-time codes, not phishing-resistant keys.
- The NIST mapping is an engineering mapping, not a compliance claim.
Discuss AccessOps
Ask about what disabling an account left behind, the leaked-key drill or how the Entra connector is kept to its test objects. Email me at aagarwalcollege@gmail.com.